
Security
Your clients trust you with their keys.
Passwords, payments, and client records live in StackOS, so we keep this page to what is true today: how your data is protected, and what we do not claim.
Secrets encrypted at rest
Website credentials, vault items, bank account numbers, and bank connection tokens are encrypted before they are stored.
A vault with its own lock
The password vault sits behind a separate passcode, on top of your sign-in. Items are shared with a client or teammate only when you choose.
Permission levels for every module
Each teammate gets a level for each part of StackOS, from none to full. Staff accounts are invite only.
View As, on the record
Owners can see StackOS exactly as a teammate sees it to check access. View As sessions are logged and cannot change data.
Clients see only their own company
The client portal shows each client their own company's projects, files, invoices, and logins, and nothing else.
Card payments through Stripe
Your clients' cards are handled by Stripe. StackOS never stores card numbers.
Staff sign-in options
Staff sign in with Google or a passkey, as well as a password.
Cookieless analytics
StackOS website analytics, including the analytics on this site, do not set cookies.
Reviewed against the product on October 17, 2026.
The vault
Shared on purpose, never by accident.
Keep every website, hosting, and service login in folders behind a passcode. Share one item with a client's portal or a teammate when you need to, and import or export the vault whenever you like.
Team, permissions, and vault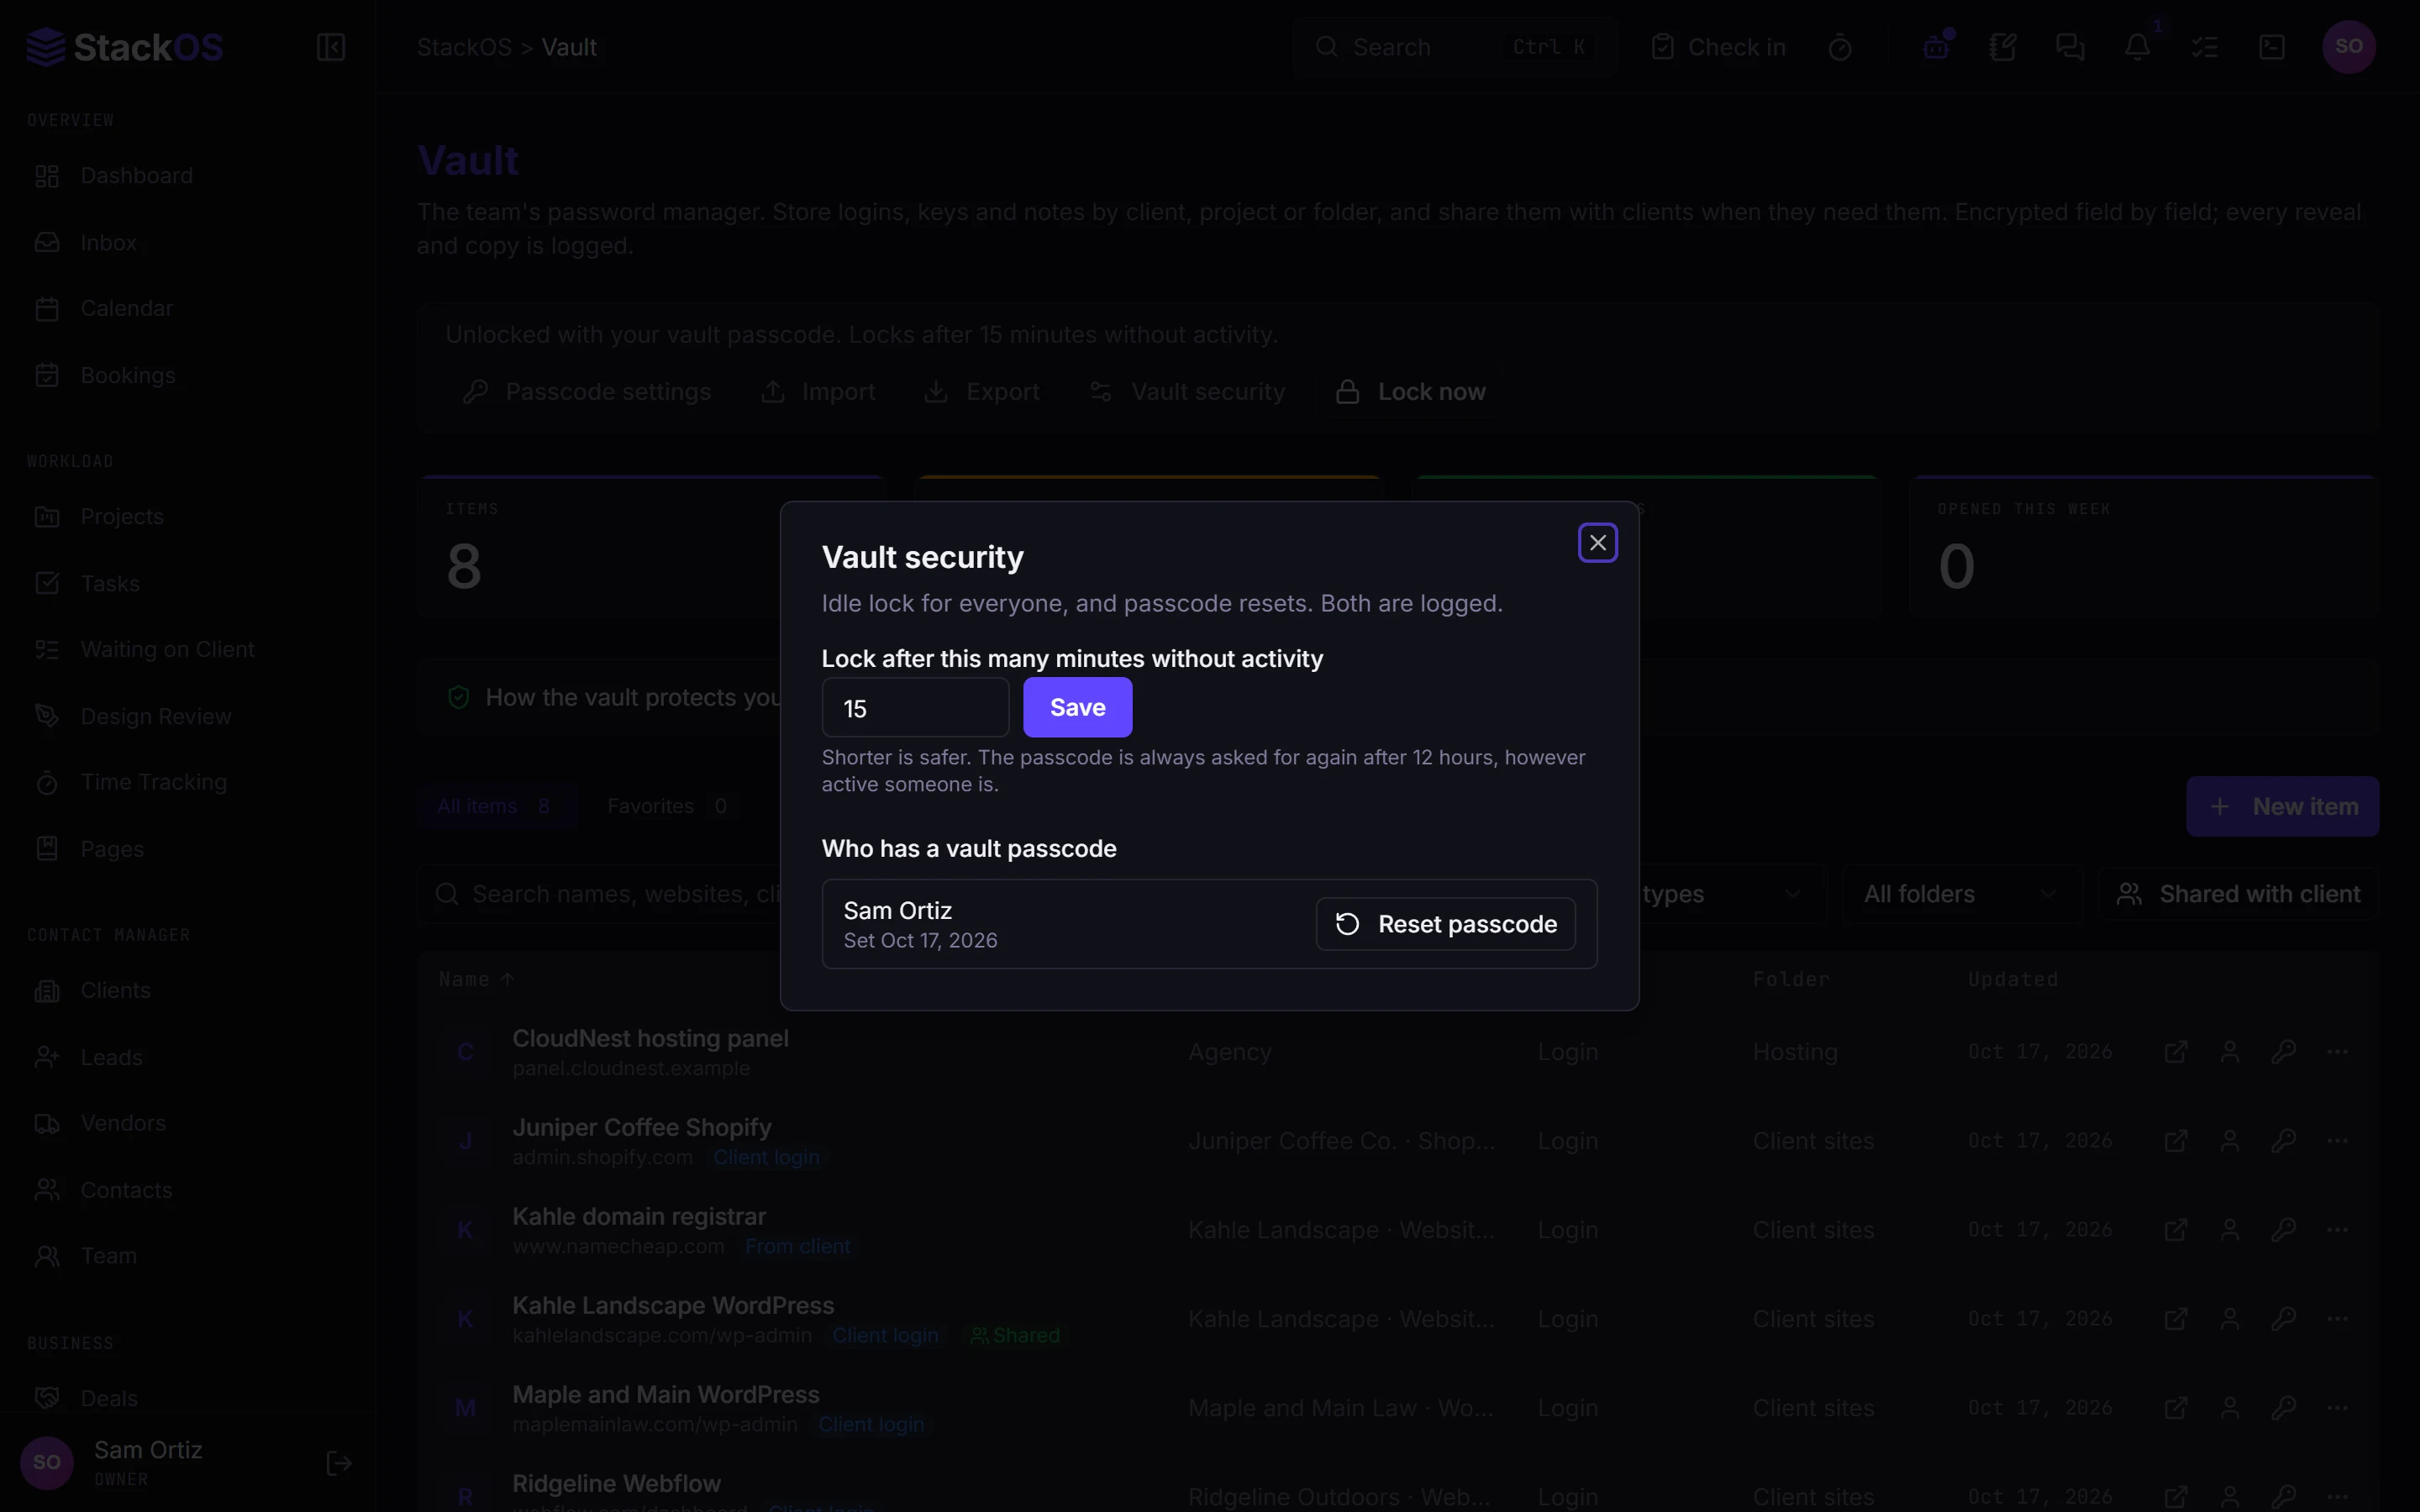
Security questions
What we do and don't claim.
Is StackOS SOC 2 certified?
Can my clients see each other's information?
How do I report a security issue?
Run your whole web studio in one place.
Start with one client. See the difference in a week.
25 web studios. Free during the beta.